2026
10
I joined Eric Woodruff and Sean Deuby on the HIP Podcast to discuss Microsoft’s Passkey Shift
07
I joined Altered Security to discuss synced passkey persistence in Azure, registration flows, detection, and remediation.
06
Find device code sign-ins and test a Conditional Access block before enforcing it.
Prefer NRPT for DNS namespace blocks to avoid shared-IP fallout from broad Firewall FQDN rules.
05
Control VS Code extensions with an enforced allowlist and keep reviewing approved extensions.
04
Limit Exchange application permissions to the mailboxes an app actually needs.
I joined Merill Fernando, Ru Campbell, and Thomas Naunheim on Entra.Chat to discuss Entra Backup, Tenant Governance, Conditional Access, and risk.
03
I joined Merill Fernando and Daniel Bradley on Entra.Chat to discuss passkeys, Conditional Access, and Global Secure Access BYOD.
I joined Merill Fernando and the Entra.Chat crew to recap Microsoft’s identity announcements at Ignite.
Sign-in Frequency (SIF) is a commonly misunderstood control, one many orgs use to inflict unnecessary suffering on their employees 😩
It probably doesn’t work the way you think it does and is often used in less than ideal ways…
So let’s look at how it works and when to use it.
Original documentation excerpt introducing sign-in frequency and the risks of repeatedly asking users for credentials. Historical November 2025 documentation screenshot. Its broad session-revocation wording must not be treated as a guarantee for every application; use current, qualified guidance.
I joined Merill Fernando and the Microsoft Entra team to discuss getting Entra Suite set up right.
Keep admin sessions separate while allowing device-based Conditional Access checks.
Find and triage domain variants that could be used to impersonate your organization.
Lets see what we can do about minimizing passkey deployment issues with Compliance and App Protection Policy requirements :)
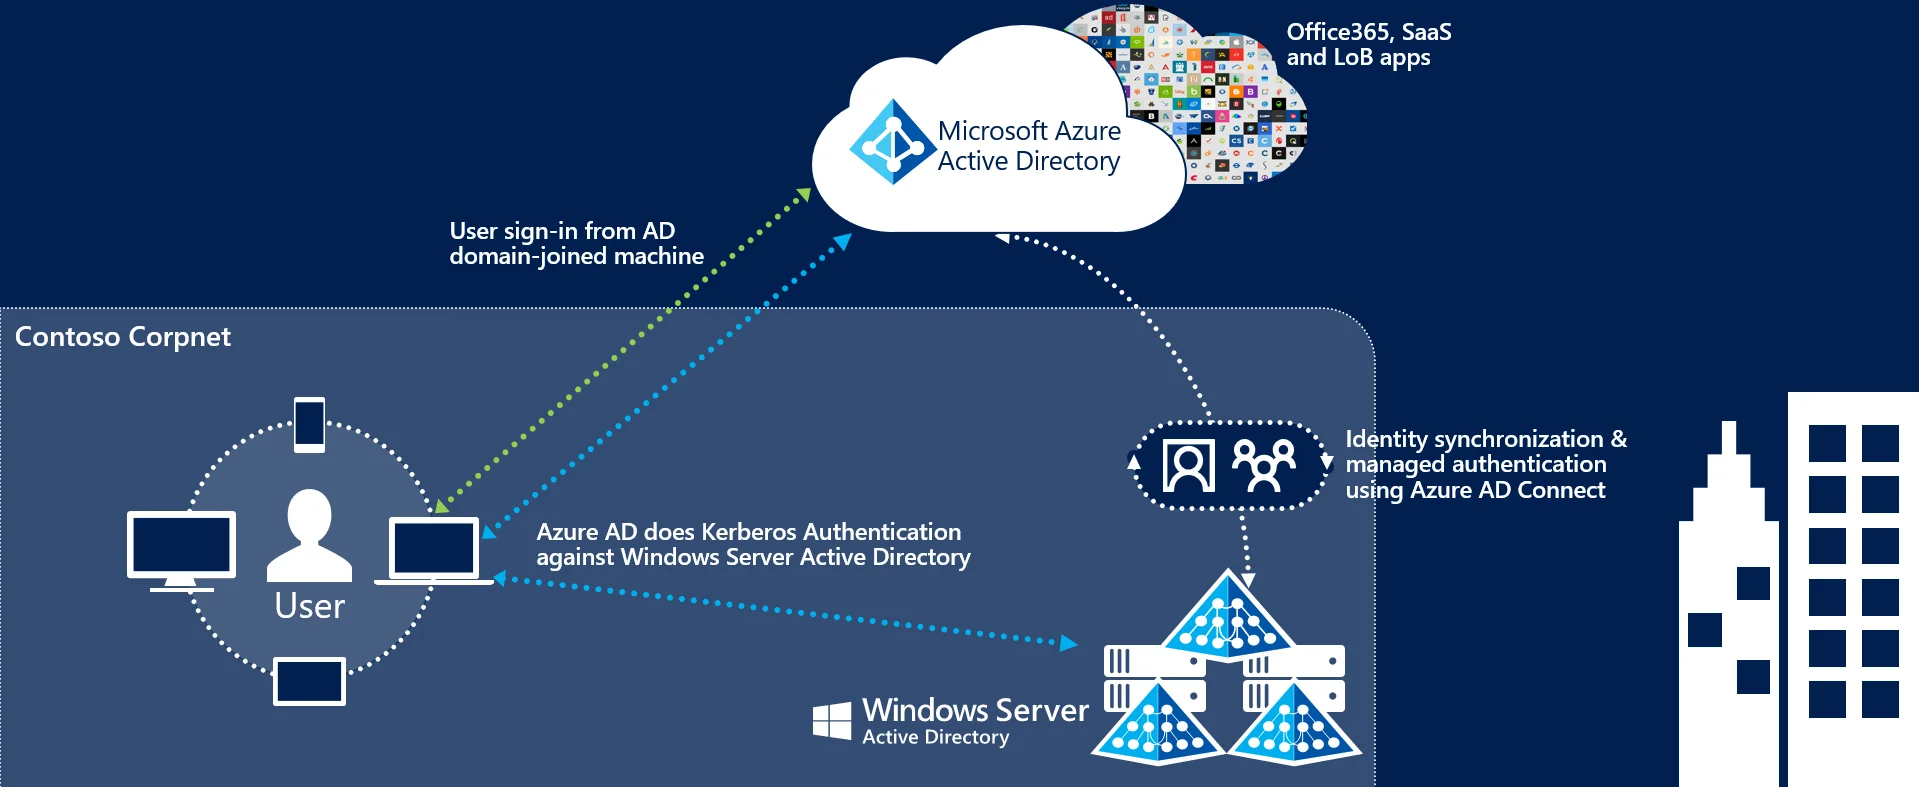
Disabling Seamless SSO is a simple checkbox, but figuring out what might break is a different story...
Review PIM security alerts for useful identity recommendations and in-portal fixes.
Skip the race to press a startup key with Windows' firmware restart switch.
This post provides everything you need to ensure Advanced Auditing is fully configured and auditing everything we possibly can for both existing and new users. I recently shared guidance for this via social media (see below), and it felt like a perfect time to revisit my previous posts and combine everything into one comprehensive guide :)
You likely aren't collecting all available events to the Unified Audit Log
First, not all events are enabled or retained optimally. Consider creating this policy in the Purview portal (leave users and record types blank to collect everything).
Retention is based on license... pic.twitter.com/IEKKfrkpI8
— Nathan McNulty (@NathanMcNulty) January 20, 2025
👮 Restricted Management Admin Units (RMAU) in #EntraID
Hackers HATE This Hidden Entra ID Feature Most Admins Never Use@NathanMcNulty breaks it down for us 👇
🎧 Get the full podcast episode at https://t.co/gnvH23WorW pic.twitter.com/nxBwCQ6BwS
— Merill Fernando (@merill) March 29, 2025 I recently had a chance to discuss Restricted Management Administrative Units (RMAUs) with Merill, and one of my favorite uses for these is to protect groups that are used in Conditional Access policies so they aren’t accidentally modified or deleted. I’m also a big fan of using Access Packages to control membership of these groups for things like exclusions from geofencing policies, user action policies, blocking policies, etc.

I joined Merill Fernando on Entra.Chat to discuss operational groups and practical ways to manage Microsoft Entra.
Keep useful Defender Antivirus notifications without all the noncritical noise.
Use monitor mode and local extension controls to limit what Azure Arc can do on your servers.
Save time on Entra rollout communications with Microsoft's customizable end-user materials.
Automate security group membership based on device hardware, software, vulnerabilities, and other inventory data
Quick tip on using workbooks to create KQL queries and get more data than provided by the workbook
Practice Defender for Identity alert investigation in an isolated, planned lab.
Ensure all available audit records are collected to Unified Audit Log
A tool to assess and automate configuration in the Defender portal
Improve Defender performance by performing one full scan
Check cloud Kerberos trust prerequisites before using Hello for on-premises SSO.