
I joined Eric Woodruff and Sean Deuby on the HIP Podcast to discuss Microsoft’s Passkey Shift

I joined Altered Security to discuss synced passkey persistence in Azure, registration flows, detection, and remediation.
I joined Merill Fernando, Ru Campbell, and Thomas Naunheim on Entra.Chat to discuss Entra Backup, Tenant Governance, Conditional Access, and risk.
I joined Merill Fernando and Daniel Bradley on Entra.Chat to discuss passkeys, Conditional Access, and Global Secure Access BYOD.
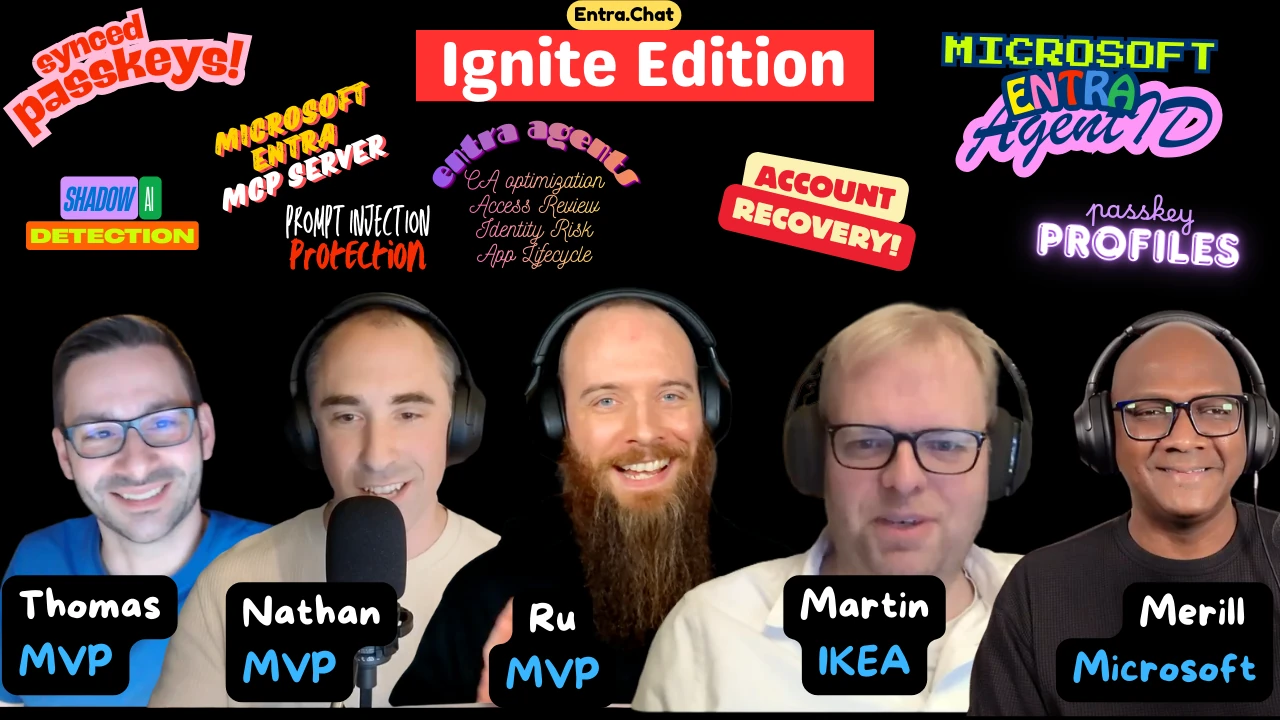
I joined Merill Fernando and the Entra.Chat crew to recap Microsoft’s identity announcements at Ignite.
I joined Merill Fernando and the Microsoft Entra team to discuss getting Entra Suite set up right.

Lets see what we can do about minimizing passkey deployment issues with Compliance and App Protection Policy requirements :)

Disabling Seamless SSO is a simple checkbox, but figuring out what might break is a different story...

This post provides everything you need to ensure Advanced Auditing is fully configured and auditing everything we possibly can for both existing and new users. I recently shared guidance for this via social media (see below), and it felt like a perfect time to revisit my previous posts and combine everything into one comprehensive guide :)
You likely aren't collecting all available events to the Unified Audit Log
First, not all events are enabled or retained optimally. Consider creating this policy in the Purview portal (leave users and record types blank to collect everything).
Retention is based on license... pic.twitter.com/IEKKfrkpI8
— Nathan McNulty (@NathanMcNulty) January 20, 2025

👮 Restricted Management Admin Units (RMAU) in #EntraID
Hackers HATE This Hidden Entra ID Feature Most Admins Never Use@NathanMcNulty breaks it down for us 👇
🎧 Get the full podcast episode at https://t.co/gnvH23WorW pic.twitter.com/nxBwCQ6BwS
— Merill Fernando (@merill) March 29, 2025 I recently had a chance to discuss Restricted Management Administrative Units (RMAUs) with Merill, and one of my favorite uses for these is to protect groups that are used in Conditional Access policies so they aren’t accidentally modified or deleted. I’m also a big fan of using Access Packages to control membership of these groups for things like exclusions from geofencing policies, user action policies, blocking policies, etc.

I joined Merill Fernando on Entra.Chat to discuss operational groups and practical ways to manage Microsoft Entra.

I joined the Trimarc team for a Happy Hour conversation about a little bit of everything.
