Ingest Azure Activity Logs into Sentinel
Collect Azure Activity Logs in Sentinel and check which tables have ingestion charges.
If you are using Azure resources, it is free to ingest Azure Activity Logs into Microsoft Sentinel. Please collect these logs and build detections :)
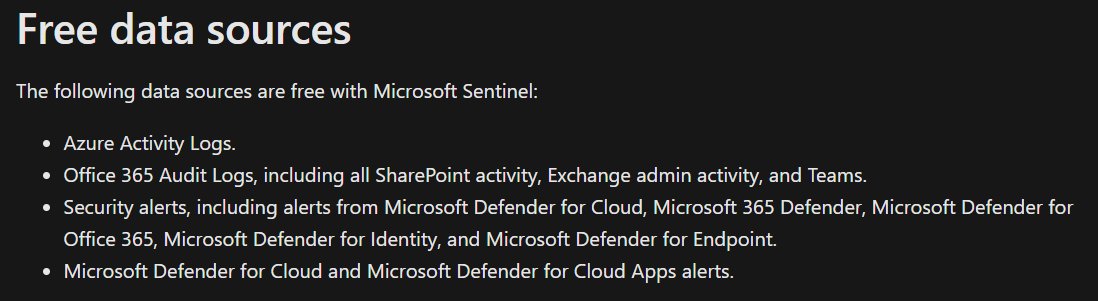
These logs record management operations such as creating resources or changing a Key Vault access policy. Export the subscription’s Activity log to a Sentinel-enabled Log Analytics workspace using a diagnostic setting. The events land in the AzureActivity table.
You can check ingestion billing in the Log Analytics workspace under Monitoring > Insights > Usage. Find AzureActivity and look at the Billable column.
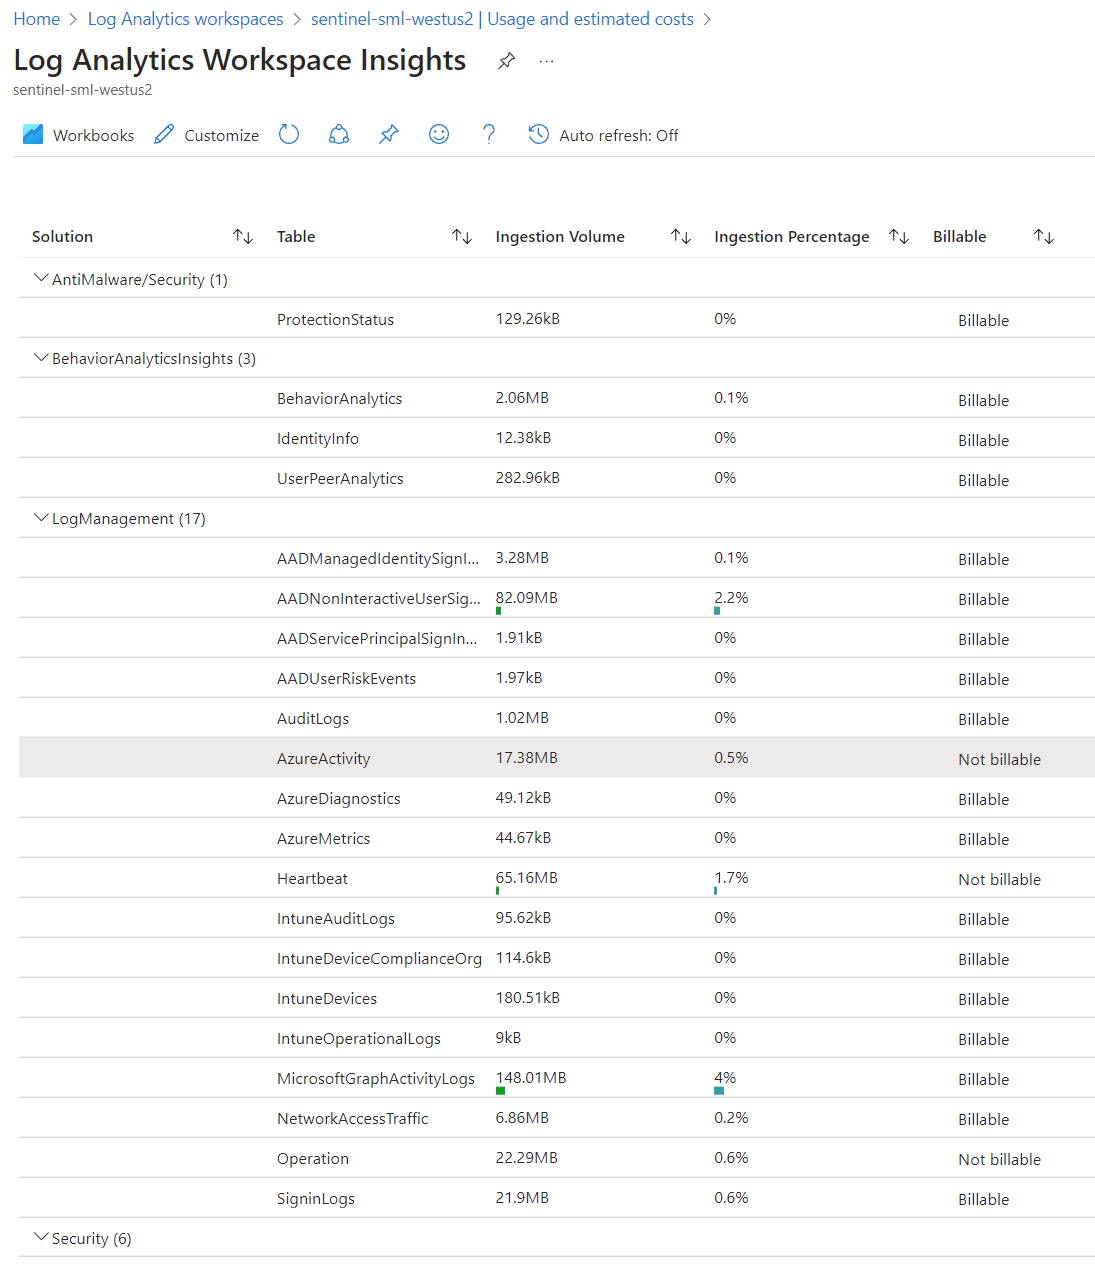
Keep an eye on retention and the other data you collect. Activity log retention beyond 90 days can add charges, and Entra sign-in and audit logs have separate ingestion costs. If you want to collect those too, I have a guide to integrating Entra logs with Azure Monitor.
This is also one of the quick wins in Azure - Securing Subscriptions.
Sentinel free data sources | Export the Activity log | Workspace usage insights
Original posts: 17 October 2023 and checking ingestion billing. Documentation checked 14 October 2026.